
In 2026, the shift from static text generation to autonomous execution has fundamentally altered how we construct LLM interactions. An agent prompt is no longer a simple instruction set; it is a high-stakes operational contract that governs reasoning, tool selection, and state transitions within a production environment.
The engineering challenge lies in balancing the agent’s autonomy with the deterministic requirements of enterprise infrastructure. When a system relies on autonomous loops to resolve complex tasks, the prompt becomes the primary mechanism for safety, guardrails, and performance. This article details the structural patterns required to move from experimental prototypes to production-ready agent deployments.
Foundational Concepts of Agent Prompt Engineering
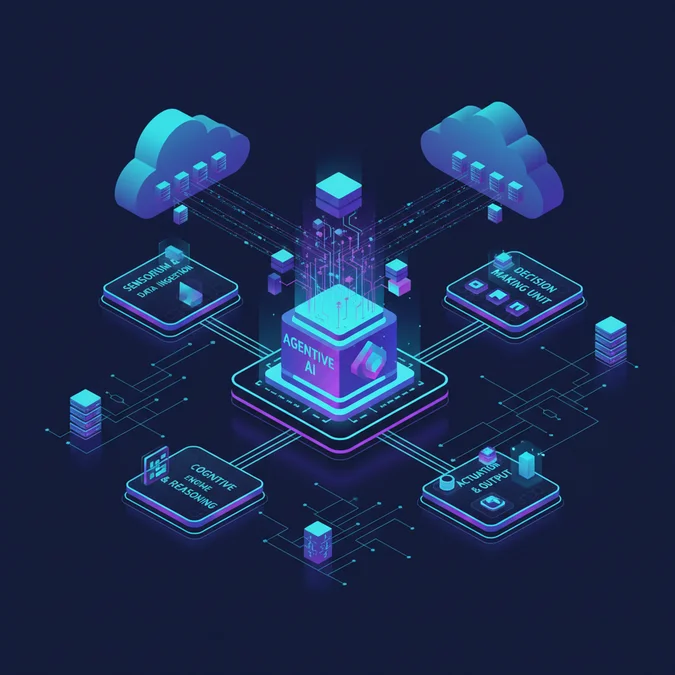
The core distinction in ai agent prompting is the transition from a stateless request-response model to a stateful, iterative cycle. Unlike standard prompts, which focus on output quality, an agent prompt must define the agent’s perception of the environment, its capability set, and the constraints of its operational loop.
Engineering Note: Agent prompts function as the ‘brain’ of the runtime loop. If the prompt fails to define clear termination criteria, the agent will inevitably enter recursive loops or hallucinate tool calls that do not exist.
Effective agent prompts must explicitly encode the following:
- Operational Persona: Defining the agent’s specific role within the system hierarchy.
- Tool Schema Awareness: Mapping available APIs to specific reasoning triggers.
- Constraint Boundaries: Explicit instructions on what the agent is forbidden from doing, such as executing external commands without secondary validation.
Designing the AI Agent System Prompt for Complex Workflows
The ai agent system prompt serves as the foundation for the agent’s decision-making process. To ensure reliability, treat the system prompt as a structured configuration file rather than natural language prose. Below is a production-grade template structure:
{ "system_role": "Data Orchestrator", "constraints": [ "No direct database writes without verification", "Always check status codes before retrying" ], "reasoning_process": "ReAct: Thought, Action, Observation, Conclusion", "tool_registry": [ "search_api", "sql_query_executor" ] }Production Checklist for System Prompts:
- Verify all tool IDs match the implementation registry exactly.
- Include a ‘recovery protocol’ for when a tool returns an error.
- Define the expected output format (JSON/XML) to ensure downstream parsing success.
- Inject current system time and environmental context as dynamic variables.
Comparative Analysis of Prompting Frameworks
Choosing the right ai agent prompting methodology significantly impacts latency and success rates. The following matrix compares standard prompting against structured reasoning frameworks.
| Framework | Complexity | Latency Cost | Reliability |
|---|---|---|---|
| Zero-Shot | Low | Low | Poor |
| ReAct | Medium | Moderate | High |
| Plan-and-Solve | High | High | Superior |
For high-throughput systems, ReAct remains the industry standard, providing a balance between reasoning depth and execution speed. Plan-and-Solve architectures are recommended only for long-running, multi-step workflows where task dependencies are non-linear.
Implementation Patterns for Tool-Use and Task Delegation
The agent prompt must facilitate precise tool selection. When an agent manages multiple tools, the prompt should enforce a single-action constraint to prevent parallel execution errors. Follow these steps for implementation:
- Define tool intent within the prompt using clear, verb-based descriptions.
- Force the model to output a specific JSON structure for every action.
- Validate tool outputs against the schema before feeding them back into the context.
// Example of a constrained tool-use prompt segment
"instructions": "You must call exactly one tool at a time. Output the action in the following JSON format: {"tool": "name", "args": {}}"
Debugging and Optimizing Agent Prompt Performance
Debugging an ai agent system prompt requires observational logs. When an agent gets stuck in a loop, the failure is usually due to an ambiguous state definition. Use this checklist to mitigate hallucinations:
- Traceability: Log the full reasoning chain for every failed iteration.
- Guardrails: Implement a ‘max_steps’ parameter to force termination.
- Verification: Add a ‘critique’ phase where the agent reviews its own proposed action before execution.
- Schema Validation: Use Pydantic or similar libraries to validate the agent’s tool-call responses before the system executes them.
Factors That Affect Development Cost
- Token usage for recursive reasoning loops
- Complexity of tool integration layers
- Latency requirements for real-time decision making
- Infrastructure overhead for state management
Costs scale linearly with the number of reasoning steps and the volume of context processed by the model.
Frequently Asked Questions
What is the primary difference between a standard prompt and an agent prompt?
An agent prompt is designed for autonomous decision-making loops, incorporating tool-use schemas, state management instructions, and reasoning constraints. Unlike standard prompts that target a single response, agent prompts define the operational boundaries and environmental interaction rules necessary for the agent to execute multi-step workflows independently.
How do I structure an ai agent system prompt for better reliability?
Structure your ai agent system prompt by clearly defining the agent identity, available tools, task constraints, and explicit error-handling procedures. Implement a structured format like YAML or JSON within the prompt to ensure the model consistently outputs machine-readable commands for tool execution and state updates.
Why is ai agent prompting considered a specialized skill set?
Ai agent prompting requires understanding stateful reasoning, context window management, and iterative feedback loops. Practitioners must move beyond simple text generation to master prompt engineering for logic-heavy architectures, balancing instruction clarity with the flexibility required for the agent to recover from unexpected tool output errors.
Designing for agents is fundamentally different from designing for chat interfaces. By treating the prompt as an architectural component of your codebase, complete with schema validation, state management, and strict operational boundaries, you can create systems that are both highly autonomous and reliably performant.
As you scale, continue to iterate on your prompt library, benchmarking each change against your specific operational requirements to maintain the desired balance of cost, latency, and accuracy.