
A distributed system design diagram fails when it hides runtime failure domains behind ambiguous boxes and unlabeled arrows. When an upstream payments gateway times out during peak load, a diagram that groups fifteen microservices into an unannotated cloud provides zero operational clarity for incident responders or RFC reviewers. Production software architecture is defined by its boundaries, synchronous dependencies, and persistence guarantees, not static visual art.
Engineering organizations waste thousands of hours debating Request for Comments (RFC) proposals simply because authors conflate conceptual business flows with physical runtime topology. When network protocols, buffer boundaries, and fallback paths are omitted, implementation teams make divergent assumptions that inevitably surface as production incidents.
This architectural guide provides a concrete, repeatable framework for drafting technical diagrams that survive operational scale. We establish standard modeling taxonomies, walk through the C4 abstraction model, construct an end-to-end event-driven transaction pipeline, and automate diagram drift prevention directly inside continuous delivery pipelines.
Architectural Taxonomy: High Level Architecture Diagram vs Functional Layers
Engineers often conflate different abstraction tiers when authoring technical design documentation. A single canvas that mixes React components, Kubernetes pods, DNS load balancers, and third-party SaaS APIs creates cognitive overload and obscures systemic failure modes. To communicate architectural intent with technical precision, you must decouple your system views into three distinct operational planes: High-Level Architecture (HLA), Functional Architecture, and Physical Infrastructure Topology.
Architectural Rule: Never mix logical capabilities with runtime infrastructure within the same abstraction viewport. If an arrow crosses both a business workflow boundary and an IP subnet perimeter simultaneously, split the representation into discrete diagrams.
A high level architecture diagram establishes the global system context. It provides executive stakeholders, security review boards, and peer engineering squads an immediate visual index of core platform capabilities. In this viewport, details like specific message serialization formats or database replica topologies are deliberately abstracted away. The objective is to define external consumers, overarching system boundaries, and primary upstream and downstream SaaS dependencies.
Conversely, a software functional architecture diagram isolates business logic domains, domain-driven design (DDD) bounded contexts, and internal module interactions. It deliberately ignores the physical infrastructure where services execute. Whether a service runs as an AWS Lambda function, a long-lived Go binary on a bare-metal server, or a container managed by Kubernetes is irrelevant to a functional view. Instead, this layer maps domain entities, command-query responsibility segregation (CQRS) boundaries, and deterministic data contracts.
Between these layers sits the software system diagram, bridging business logic with physical reality by defining communication interfaces, message queue semantics, and persistent datastores. The following matrix outlines the core trade-offs, target audiences, and technical scopes across each diagram category:
| Dimension | High Level Diagram (HLA) | Software Functional Architecture | Physical Deployment Diagram |
|---|---|---|---|
| Primary Audience | Staff+ Architects, Engineering Directors, Product Leads | Senior Software Engineers, Tech Leads, QA Architects | DevOps Engineers, Site Reliability Engineers, Platform Teams |
| Scope of Abstraction | Macro view across multiple corporate domains and external vendors | Logical software modules, domain services, and event interfaces | Physical VMs, Kubernetes clusters, VPCs, CIDR blocks, subnets |
| Communication Detail | Generalized protocols (e.g. HTTPS, Public Internet, Webhook) | Detailed interface contracts (e.g. REST, gRPC, Protobuf schema) | Network hops, TLS termination, egress gateways, proxy layers |
| Failure Mode Visibility | Third-party vendor outages, global network ingress failure | Transaction rollback, domain validation errors, cache misses | AZ partition, node OOM, pod evictions, disk I/O exhaustion |
| Drift Vulnerability | Low (conceptual platform shifts occur over multi-year cycles) | Medium (evolves with domain models and product feature sets) | High (shifts with every IaC apply, helm release, or cloud update) |
Selecting the wrong visual topology leads directly to architectural friction. When authoring an RFC, begin with a disciplined high level diagram to anchor cross-team alignment. Once the systemic boundaries are agreed upon, transition directly into functional and physical views to expose implementation trade-offs.
The C4 Framework: Structuring Every Software Architect Diagram
To eliminate ambiguity across technical teams, modern engineering organizations rely on standardized abstraction models. The industry benchmark for structuring a software architect diagram is the C4 model, developed by Simon Brown. C4 functions like Google Maps for complex codebases, allowing engineers to dynamically zoom between macro platform views and granular runtime code execution without losing architectural context.
When crafting software architecture diagrams, standardizing on C4 guarantees that team members evaluate designs against consistent cognitive rules rather than arbitrary box-and-arrow aesthetics. A rigorous diagram of software engineering must progress systematically through four descending abstraction levels:
- Level 1: System Context: Illuminates the system under design as an isolated box surrounded by human personas and external dependencies. This layer answers who uses the platform and what external systems it interfaces with. Low-level details such as communication protocols, internal thread pools, or data structures are explicitly prohibited.
- Level 2: Container Diagram: Zooms inside the system boundary to expose runnable deployment units. In C4 terminology, a container represents a runtime executable: a client single-page application, an API gateway, a microservice binary, a message broker, or a relational database cluster. Every line must document the transport protocol (such as gRPC/HTTP/2 or AMQP) and security boundaries.
- Level 3: Component Diagram: Zooms inside an individual container to reveal modular architectural decomposition. This level visualizes how controllers, repositories, event listeners, and business logic coordinators link together. This tier is essential for multi-team codebases to enforce clear separation of concerns.
- Level 4: Code Diagram: Visualizes code-level artifacts, such as Unified Modeling Language (UML) class diagrams, entity-relationship models, or state transition machines. In modern production environments, Level 4 is rarely hand-drawn. Instead, it is generated directly on-demand from interface definitions, database migrations, or AST parsing tools to prevent immediate documentation drift.
Before committing any architecture diagram to your engineering wiki or design RFC repository, validate the artifact against this structural readiness checklist:
- [ ] Explicit Directionality: Every relationship line features clear, single-directional or bidirectional arrowheads showing caller-versus-callee dynamics.
- [ ] Transport Protocol Labels: Every line denotes the wire protocol and payload format (e.g. JSON/HTTPS, Protobuf/gRPC, Avro/Kafka).
- [ ] Boundary Demarcation: Virtual Private Clouds (VPCs), Kubernetes namespaces, and third-party vendor boundaries are visually isolated using explicit bounding boxes.
- [ ] Stateful Identification: Stateful components (PostgreSQL, Redis, Kafka) are visually distinguished from stateless computing instances (API pods, background workers).
- [ ] Authentication/Authorization Context: Every ingress vector displays its security mechanism (e.g. mTLS, OAuth 2.0 Bearer Token, AWS SigV4).
From Inception to Code: Step-by-Step Program Design Diagram Blueprint
Transforming complex product requirements into an actionable program design diagram requires a methodical process. Engineering teams frequently fail during this phase by jumping straight into diagramming software without first mapping runtime state transitions and edge cases. A complete program diagram architecture must serve as an executable blueprint that any senior engineer can translate into production code without ambiguity.
When constructing software design diagrams, follow this four-stage engineering sequence to maintain technical rigor from the initial requirements review to implementation:
- Isolate State Mutability and Edge Ingress: Determine where untrusted client traffic enters the platform and where canonical mutations are permanently committed. Every write operation must traverse an idempotency layer to guard against network retries.
- Draft the Ingress-to-Persistence Core: Construct a simple system design diagram showing only the happy path. Focus strictly on API entry, synchronous validation, database write, and response return. Avoid cluttering this initial phase with async workers or analytics pipelines.
- Layer Async Side Effects and Event Buffering: Extract secondary concerns (notifications, analytics, downstream index hydration) away from the synchronous request path and place them behind resilient message queues or append-only distributed event logs.
- Define Failure Domains and Degradation Circuits: Annotate timeout thresholds, retry backoff algorithms, fallback dead-letter queues (DLQ), and circuit-breaker patterns for every network boundary.
To illustrate this implementation flow, consider an authorization check sequence inside an edge API gateway. The following PlantUML declaration generates a precise sequence diagram that models circuit breakers, Redis token cache reads, and database fallbacks:
Production Walkthrough: Sample Software Architecture Diagram for Event-Driven Microservices
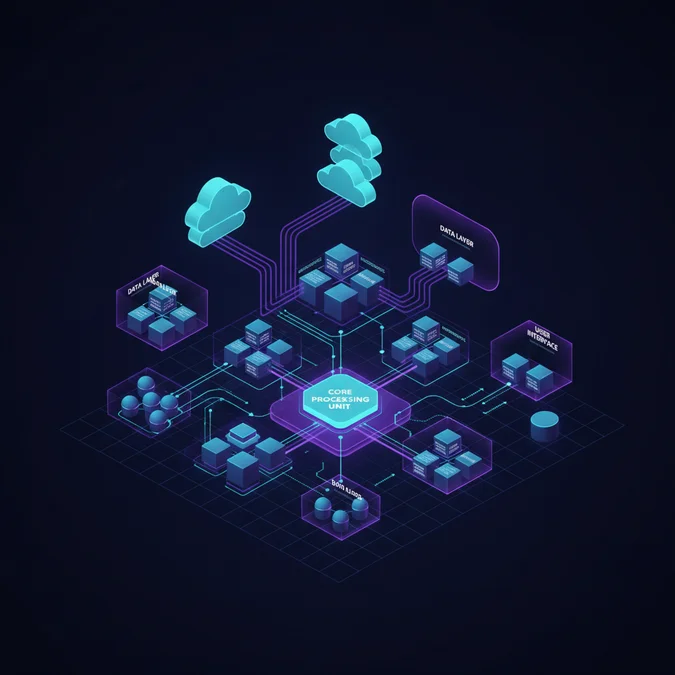
To understand the mechanics of production-ready documentation, let us examine an end-to-end sample software architecture diagram for an ultra-reliable FinTech ledger system. This distributed pipeline processes high-volume debit transactions while guaranteeing zero lost writes, idempotent processing, and horizontal read scaling.
In this architecture, incoming write requests pass through an API gateway that validates JSON Web Tokens and enforces token-bucket rate limits. Requests enter the Transaction Ingress Service, which immediately appends an uncommitted ledger row to an Amazon Aurora PostgreSQL database alongside an Outbox event entry within the exact same ACID database transaction. A dedicated transaction tailer (such as Debezium or a native outbox worker) reads write-ahead logs (WAL) and publishes these records to Apache Kafka.
Diagram-as-Code Workflows: Preventing Architectural Drift in CI/CD
The core vulnerability of visual documentation is architectural drift. Static images produced in manual canvas applications begin to rot the moment an engineer merges a pull request that introduces an undocumented message queue, splits a database read-replica, or deprecates a REST route. To make every system design architecture diagram a reliable source of operational truth, high-velocity engineering organizations treat their diagrams as version-controlled code artifacts.
By migrating your documentation to plain-text Diagram-as-Code (DaC) formats like PlantUML, Mermaid.js, or Structurizr DSL, architecture diagrams live in the same Git repositories as your application source code. When a service interface changes, the developer must update both the implementation code and the corresponding system design diagram within the exact same pull request. This workflow transforms documentation reviews into an automated, enforceable phase of your deployment pipeline.
The following GitHub Actions workflow demonstrates how to automate PlantUML compilation and linting upon pull request creation, ensuring that stale diagrams never reach your production documentation branch:
Frequently Asked Questions
What is the primary difference between a system design diagram and a software architecture diagram?
A system design diagram emphasizes multi-tier infrastructure, showing physical boundaries, networks, storage engines, and message queues. In contrast, software architecture diagrams focus on software structural abstractions, internal module relationships, domain models, and class hierarchies within that physical infrastructure.
What makes a simple system design diagram effective for engineering design reviews?
An effective simple system design diagram minimizes cognitive load by isolating a single abstraction level, standardizing directional arrows with explicit communication protocols (such as gRPC or HTTPS), and clearly demarcating stateful dependencies without cluttered low-level implementation noise.
Why should engineering teams adopt Diagram-as-Code for their technical documentation?
Diagram-as-Code tools store visual architecture diagrams as plain text directly alongside application code repositories. This allows engineers to version-control changes, run pull-request peer reviews on structural shifts, and eliminate out-of-date documentation drift automatically using continuous integration pipelines.
When should an architect use a high level architecture diagram instead of a component diagram?
Use a high level architecture diagram during initial stakeholder reviews and cross-team alignment to map systemic boundaries, major external dependencies, and overarching data flows. Reserve low-level component diagrams for implementation RFCs where developers need explicit module interfaces.
What are critical engineering considerations for sample system architecture diagram?
When implementing sample system architecture diagram, prioritize deterministic execution, rigorous error handling, observability metrics, and strict security isolation to maintain production reliability and eliminate latency bottlenecks.
What are critical engineering considerations for software architecture diagram examples?
When implementing software architecture diagram examples, prioritize deterministic execution, rigorous error handling, observability metrics, and strict security isolation to maintain production reliability and eliminate latency bottlenecks.
What are critical engineering considerations for system software architecture diagram?
When implementing system software architecture diagram, prioritize deterministic execution, rigorous error handling, observability metrics, and strict security isolation to maintain production reliability and eliminate latency bottlenecks.
A production-ready system design diagram is not decorative art. It is an operational contract that clarifies service boundaries, models distributed failure modes, and communicates the performance characteristics of your platform. By moving beyond ambiguous, ad-hoc whiteboard snapshots and committing to disciplined frameworks like C4 and Diagram-as-Code, engineering teams can align stakeholders, simplify peer RFC reviews, and prevent systemic outages.
As distributed architectures grow more complex across edge networks, multi-region clusters, and asynchronous event streams, visual precision becomes a core engineering discipline. Treat your architectural documentation with the same engineering rigor, version control standards, and automated CI validation that you demand from production code.
References & Further Reading