
Heroku deployment is an automated platform-as-a-service process that packages application code into isolated Linux containers called dynos using specialized buildpacks, orchestrating web servers, database connections, background workers, and release phases through a declarative Git push workflow. This approach eliminates standard server configuration while enforcing cloud infrastructure standards across your software development lifecycle.
Shipping a modern PHP application like Laravel to containerized infrastructure presents acute operational friction. Teams regularly encounter ephemeral filesystem wipes that delete uploaded assets, misconfigured reverse proxies that corrupt protocol detection and HTTPS redirects, failing database migrations that stall deployment pipelines, and background job starvation when queuing configurations default to local sync drivers instead of remote brokers.
Resolving these infrastructure bottlenecks requires structuring Laravel specifically for twelve-factor architecture. By standardizing configuration management, delegating persistence to dedicated cloud services, and establishing predictable deployment release steps, engineering teams can achieve resilient automated rollouts on Heroku with near-zero downtime.
Heroku Architecture and Dyno Mechanics for Laravel
Deploying Laravel to Heroku fundamentally alters how the PHP runtime interacts with the host environment. Traditional virtual machines run persistent file systems, systemd services, and long-lived cron daemons. Heroku executes workloads inside dynos: isolated, ephemeral Linux containers running on an underlying Amazon Web Services Elastic Compute Cloud (AWS EC2) substrate. Understanding how dynos operate is mandatory for stabilizing application behavior.
The Ephemeral Filesystem and Local Storage Failures
Every dyno operates with an ephemeral filesystem. When a dyno restarts, deploys new code, or cycles daily during automatic platform maintenance, all writes to the local file system vanish completely. Storing user uploads, generated invoice PDFs, or application cache files in Laravel’s default storage/app/public directory results in catastrophic data loss upon restart. Media assets and permanent files must stream directly to cloud object storage like Amazon S3 or Google Cloud Storage using Laravel’s cloud filesystem driver.
// config/filesystems.php
'disks' => [
 's3' => [
 'driver' => 's3',
 'key' => env('AWS_ACCESS_KEY_ID'),
 'secret' => env('AWS_SECRET_ACCESS_KEY'),
 'region' => env('AWS_DEFAULT_REGION'),
 'bucket' => env('AWS_BUCKET'),
 'url' => env('AWS_URL'),
 'endpoint' => env('AWS_ENDPOINT'),
 'use_path_style_endpoint' => env('AWS_USE_PATH_STYLE_ENDPOINT', false),
 'throw' => true, // Throw exceptions on failed S3 operations for immediate pipeline visibility
 ],
],
Log files written to local disk are similarly wiped. Heroku requires applications to aggregate logs over stdout and stderr. Dyno log streams capture these outputs and forward them to Heroku Logplex, which routes them to external aggregators such as Datadog, Papertrail, or Logstash for persistence.
Process Formation and the Procfile
Dynos organize around a declarative process formation defined in a root-level Procfile. This plain-text manifest tells Heroku which commands run when booting specific process types. Laravel requires distinct dyno types to isolate web traffic from asynchronous operations, avoiding CPU contention between request handling and long-running database tasks.
- web: Handles HTTP ingress, serving PHP via Apache or Nginx combined with PHP-FPM.
- worker: Executes queue worker loops via artisan commands to process asynchronous workloads.
- release: Runs single-off tasks immediately after a successful build before new dynos receive user traffic.
Configuring the Web Server with Custom Nginx Directives
Heroku’s official PHP buildpack contains standard Nginx and Apache runtime binaries, but Laravel’s internal front-controller pattern requires precise web server rules to avoid runtime routing failures. By default, requests must route entirely through public/index.php while preserving query parameters and handling static assets efficiently.
To run Nginx instead of Apache, configure the web dyno process in your Procfile to point to a custom Nginx configuration file. This guarantees complete control over HTTP headers, timeouts, gzip compression, and static asset caching policies.
# Procfile definition for production Laravel
web: vendor/bin/heroku-php-nginx -C nginx.conf public/
worker: php artisan queue:work --sleep=3 --tries=3 --max-time=3600 --memory=128
release: php artisan migrate --force
The custom nginx.conf file instructs Nginx to capture Laravel’s routing requirements. Include the configuration block directly in the root of your repository:
# nginx.conf
location / {
 # Direct all requests to index.php if static file does not exist
 try_files $uri $uri/ /index.php?$query_string;
}

# Optimize asset delivery
location ~* \.(jpg|jpeg|gif|png|css|js|ico|svg|woff2)$ {
 expires 30d;
 add_header Cache-Control "public, no-transform";
 try_files $uri =404;
}

# Secure hidden files
location ~ /\.(?well-known).* {
 deny all;
}
Heroku operates a routing mesh that handles TLS termination upstream, forwarding requests to dynos over unencrypted internal HTTP connections while injecting proxy headers such as X-Forwarded-For and X-Forwarded-Proto. Without instructing Laravel to trust these upstream proxies, applications generate invalid URLs, drop security cookies, and face broken state handling. Teams troubleshooting upstream proxy headers and session loss often discover that correcting proxy trust settings resolves deep authentication hurdles, including troubleshooting cross-site token failures in distributed deployments.
Ensure your application trusts Heroku load balancers inside bootstrap/app.php or within the dedicated middleware layer:
// In Laravel 11 bootstrap/app.php
->withMiddleware(function (Middleware $middleware) {
 $middleware->trustProxies(at: '*'); // Trust all Heroku routing mesh ingress nodes
})
Step-by-Step Laravel Deployment Guide via Heroku CLI
Deploying a production Laravel project requires executing specific commands to initialize platform resources, install environment variables, and trigger compilation pipelines. Follow this sequential operational roadmap.
- Authenticate and Initialize Application: Log in to the platform and provision a new application container within your chosen geographical region.
# Authenticate via terminal heroku login # Provision app in the European or United States region heroku create production-laravel-api --region us - Attach Language and Node Buildpacks: Laravel applications require two distinct compilation targets: the PHP runtime engine and a Node.js runtime to compile frontend assets using Vite or Mix.
# Add Node.js buildpack first for asset compilation heroku buildpacks:add --index 1 heroku/nodejs # Add PHP buildpack as the final execution environment heroku buildpacks:add --index 2 heroku/php - Configure Essential Environment Variables: Set the foundational configuration flags. Never commit sensitive encryption keys to your Git repository; inject them directly into Heroku config vars.
# Set production environment flags heroku config:set APP_ENV=production heroku config:set APP_DEBUG=false heroku config:set APP_KEY=$(php artisan --dry-run key:generate --show) heroku config:set LOG_CHANNEL=errorlog - Configure Composer Dependencies and Scripts: Instruct Heroku’s PHP buildpack to run production optimizations during deployment by defining a compile script inside
composer.json. This runs config caching and route compiling before dynos switch over to the new release artifact."scripts": { "post-install-cmd": [ "Illuminate\\Foundation\\ComposerScripts:postInstall", "@php -r \"file_exists('.env') || copy('.env.example', '.env');\"" ], "heroku-postbuild": [ "npm install --prefer-dist --no-progress", "npm run build", "php artisan config:cache", "php artisan route:cache", "php artisan view:cache" ] } - Deploy the Codebase: Push your local mainline branch directly to the Heroku Git remote to kick off the slug compiler.
# Push to Heroku remote branch
git push heroku main
For teams seeking mature deployment patterns beyond manual Git pushes, evaluating automated pipelines like a custom programmatic infrastructure orchestration flow highlights the architectural trade-offs between managed PaaS platforms and automated bare virtual machines.
Managing Database Connections, Migrations, and Persistent Cache
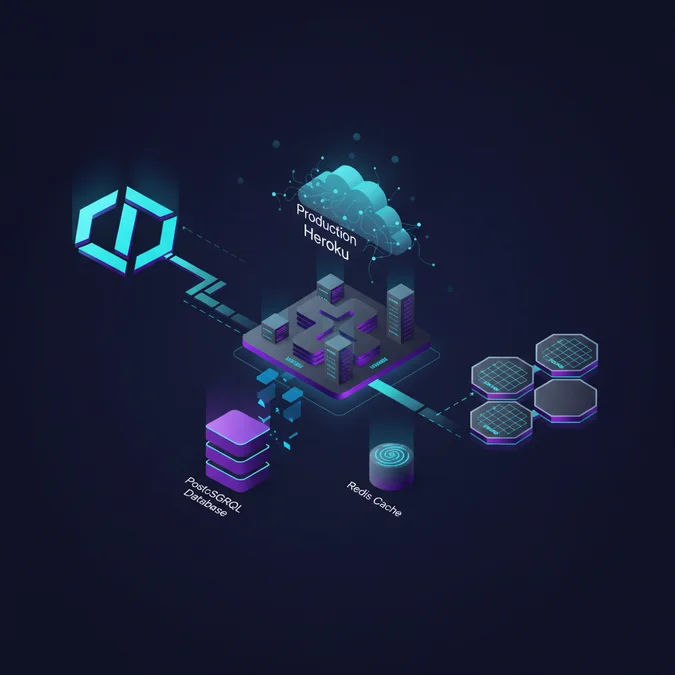
A functional Laravel application requires relational database engines and in-memory caches. Heroku does not bundle databases inside dynos. You must provision managed platform data services and bind them to dyno configuration variables.
Provisioning Heroku Postgres and Redis
Execute platform CLI commands to attach production-ready Postgres and Redis instances. Heroku injects connection URI strings directly into your application runtime environment variables.
# Provision managed PostgreSQL (Essential-0 for dev, Standard-0+ for production)
heroku addons:create heroku-postgresql:essential-0

# Provision managed Heroku Data for Redis
heroku addons:create heroku-redis:mini
Mapping Connection URLs into Laravel Configuration
Heroku provides database and cache connection strings as single URL strings (for example, DATABASE_URL and REDIS_URL) rather than separate host, port, username, and password fields. Laravel’s default configuration files handle connection URLs cleanly without manual parsing logic.
// config/database.php - PostgreSQL block
'pgsql' => [
 'driver' => 'pgsql',
 'url' => env('DATABASE_URL'), // Native parsing handles protocol, host, port, credentials
 'database' => env('DB_DATABASE', 'forge'),
 'schema' => 'public',
 'sslmode' => 'require', // Enforce encrypted communication between dynos and Postgres
],
For Redis connections, ensure the configuration uses the URL string directly while securing the connection via TLS when required by Heroku Redis plans:
// config/database.php - Redis block
'redis' => [
 'client' => env('REDIS_CLIENT', 'phpredis'),
 'default' => [
 'url' => env('REDIS_URL'),
 'host' => env('REDIS_HOST', '127.0.0.1'),
 'port' => env('REDIS_PORT', '6379'),
 'database' => env('REDIS_DB', '0'),
 ],
],
Automating Migrations with the Release Phase
Running database migrations directly inside active web or worker dynos causes critical race conditions if multiple dynos boot concurrently. Performing migrations manually over SSH invites human error and creates deployment bottlenecks. Heroku solves this via the release phase in the Procfile.
When specified, the release command executes inside a temporary, isolated dyno spun up immediately after build completion. If the command succeeds (exit code 0), Heroku shifts network traffic to the newly created web dynos. If the release phase fails, such as when a database constraint fails during a migration, the deployment terminates immediately. The existing production release continues serving traffic without interruption.
# Procfile definition ensuring migrations pass before rollout
release: php artisan migrate --force
Handling Asynchronous Workloads and Background Workers
A high-performance Laravel backend must offload heavy operations like transactional email delivery, webhook broadcasting, and data exports to asynchronous background queues. Attempting to process these inside the web dyno’s synchronous HTTP cycle exhausts web server execution limits and introduces high request latency.
Configuring Worker Dynos
Scale dedicated worker dynos to process jobs from your Redis queue backend. Unlike web dynos that listen on an assigned $PORT environment variable, worker dynos run persistent CLI worker daemons.
# Scale worker dyno to 1 running instance
heroku ps:scale worker=1
The artisan worker command must include operational flags to prevent container crashes, manage system memory usage, and handle dyno restarts cleanly:
# Standard production queue execution
php artisan queue:work redis --sleep=3 --tries=3 --max-time=3600 --memory=128
The --max-time=3600 flag terminates the worker process every hour. Because PHP CLI scripts can suffer from incremental memory leaks over days of execution, this deliberate lifecycle termination allows the dyno process supervisor to restart a fresh artisan worker instance cleanly. The --memory=128 flag protects standard dynos (which offer 512MB of RAM on basic tiers) from catastrophic out-of-memory errors that trigger container reboots.
Managing Scheduled Tasks via Heroku Scheduler
Standard Linux servers run cron daemons to drive Laravel’s schedule runner (php artisan schedule:run). Dynos do not run continuous cron services. Instead, provision the Heroku Scheduler add-on.
# Provision free scheduling utility
heroku addons:create scheduler:standard

# Open scheduler dashboard to define triggers
heroku addons:open scheduler
Within the Scheduler dashboard, define a job running every 10 minutes that executes the command:
php artisan schedule:runFor tasks requiring sub-minute precision or continuous event dispatching, organizations often abandon polling setups in favor of persistent daemon processes or real-time event distribution. When developing interactive systems, reviewing how event streaming operates under low-latency real-time state synchronization offers valuable insights into running stateful network services alongside standard web workers.
Comprehensive Cost Analysis and Pricing Models for Heroku Deployments
Understanding the exact financial requirements of deploying on Heroku is necessary to project operating expenses accurately as traffic expands. Heroku utilizes a tiered pricing architecture based on resource consumption across dynos, databases, and managed caching services.
Dyno and Add-on Infrastructure Costs
Unlike raw infrastructure providers where costs relate directly to unmanaged compute instances, Heroku bundles managed runtime maintenance, automated patch orchestration, and container tooling into its platform costs.
| Resource Tier | Compute / Memory Specs | Platform Function | Monthly Cost Range |
|---|---|---|---|
| Eco & Basic Dynos | Shared vCPU, 512 MB RAM | Staging, prototypes, non-critical workers | $5.00 – $7.00 per dyno |
| Production Dyno (Standard-1X) | Shared vCPU, 512 MB RAM | Small production web / queue workers | $25.00 – $50.00 (1-2 dynos) |
| Production Dyno (Standard-2X) | Shared vCPU, 1024 MB RAM | Medium enterprise API traffic, heavy queues | $50.00 – $150.00 (1-3 dynos) |
| Performance Dynos (Performance-M/L) | Dedicated vCPU, 2.5 GB – 14 GB RAM | High-throughput web traffic, zero cold starts | $250.00 – $500.00+ per dyno |
| Heroku Postgres (Essential to Standard) | Shared to Dedicated RAM, HA failover | Relational transactional storage | $5.00 to $200.00+ monthly |
| Heroku Data for Redis | 25 MB to 1 GB+ in-memory storage | Queue broker, application cache, session store | $3.00 to $60.00+ monthly |
Comparing Cloud Engineering Cost Models
When selecting deployment models, organizations must weigh direct platform fees against the cost of engineering resources required for configuration, operations, and maintenance. Engineering teams typically evaluate three primary models for provisioning and operating infrastructure:
| Engagement / Delivery Model | Typical Pricing Model | Direct Financial Commitment | Operational Overhead & Trade-offs |
|---|---|---|---|
| PaaS Deployment (Heroku Native) | Platform Subscription | $80.00 – $450.00 / month | Minimal DevOps maintenance; rapid time-to-market; higher compute premium at high scale. |
| Dedicated Cloud Consulting / Agency Retainer | Monthly Retainer | $3,500.00 – $8,000.00 / month | Outsourced infrastructure management; custom pipeline setup; higher monthly financial baseline. |
| Custom Cloud Migration Project (AWS/GCP via Terraform) | Fixed Project-Based Fee | $8,000.00 – $25,000.00 (One-time) | Lowest raw runtime compute fees; maximum control; requires senior in-house engineers to maintain. |
For low to medium traffic profiles, Heroku remains cost-effective because it reduces infrastructure maintenance hours. When dyno counts increase into dozens of Performance-tier containers, the balance often shifts toward custom orchestrations on native cloud providers.
Performance Optimization and Scaling Bottlenecks
Running Laravel inside dyno clusters introduces distinct architectural bottlenecks around memory allocation, socket reuse, and concurrency. Mitigating these limits requires optimizing how the PHP engine handles requests.
PHP-FPM Worker Tuning
Heroku’s PHP buildpack sets PHP-FPM concurrency automatically based on the dyno’s physical RAM footprint. On a Standard-1X dyno with 512 MB of memory, the default concurrency often provisions up to 5 worker processes. If your Laravel application loads massive packages, executes memory-heavy Eloquent queries, or manipulates image buffers, memory consumption can quickly exceed 100 MB per process.
When aggregate process memory crosses 512 MB, the dyno begins swapping memory to disk, leading to high response latency, request queuing, and R14 (Memory Quota Exceeded) platform errors. Override automatic concurrency detection by establishing explicit environment limits:
# Limit concurrent PHP-FPM workers per dyno to prevent memory paging
heroku config:set WEB_CONCURRENCY=3
Database Connection Pooling Limits
Horizontal scaling creates secondary bottlenecks at the database layer. If you scale your application to 10 web dynos, each running 4 PHP-FPM workers, your application can open 40 concurrent database sockets. Standard-tier PostgreSQL instances enforce strict connection ceilings (often between 20 and 120 max connections depending on plan).
Exhausting database connections triggers immediate application-wide 500 exceptions. Resolve this constraint by implementing connection pooling:
- Utilize PgBouncer, available directly through Heroku Postgres connection pooling features, by setting the
DATABASE_URLto reference the pooled port (usually 5433 or an explicit pooled environment variable provided by the platform). - Configure PDO persistent connections cautiously. Avoid long-lived persistent connections inside short-lived CLI worker cycles.
- Set database connection pool limits directly in
config/database.phpto terminate idle connections quickly.
Thorough testing of these configurations under realistic load curves prevents high-traffic failures. Rigorous automated verification strategies, like those used by independent quality assurance teams auditing enterprise infrastructure, confirm that applications handle connection limits safely before production rollout.
Monitoring, Observability, and Log Management
Diagnosing failures in containerized cloud infrastructure requires centralized observability. Because you cannot connect via traditional SSH to inspect static system log directories, your runtime health depends entirely on log streams and application metrics.
Decoding Heroku Platform Error Codes
When requests fail at the infrastructure layer, Heroku injects explicit error codes into the Logplex stream. Diagnosing production incidents requires immediate familiarity with the most common platform codes:
- H10 (App Crashed): The dyno failed to start or crashed during execution. This frequently traces to an uncaught PHP fatal error during the boot cycle or a missing
APP_KEY. - H12 (Request Timeout): An HTTP request exceeded the hard 30-second processing limit enforced by the Heroku router. Heavy database operations or long API calls must shift to background workers.
- H14 (No Web Dynos Running): The application received HTTP ingress traffic, but the web process type was scaled to 0 instances.
- R14 (Memory Quota Exceeded): The dyno exceeded its allocated RAM threshold, forcing data into swap space and degrading overall application response speed.
Stream Monitoring and Centralized Aggregation
Monitor your dyno cluster in real time using the Heroku CLI stream command:
# Follow live aggregated logs across all running dyno types
heroku logs --tail --app production-laravel-api
To retain logs long-term for audit compliance and distributed tracing, provision an external logging drain add-on such as Papertrail or Coralogix. These services capture and index raw Logplex streams automatically:
# Attach Papertrail logging drain
heroku addons:create papertrail:choklad
Combine platform log streaming with an application performance monitoring (APM) tool like New Relic, Sentry, or Scout APM. APM agents run alongside the PHP runtime, providing deep visibility into slow SQL queries, hydration bottlenecks in the Eloquent ORM, and unhandled exceptions that Logplex cannot decode on its own.
Continuous Delivery and Automated Pipelines with Heroku
Relying on manual local pushes from a developer workstation risks introducing unverified code into production. Implementing automated continuous integration and continuous deployment (CI/CD) pipelines ensures that all tests pass, security scans succeed, and assets compile correctly before dynos update.
Heroku Pipelines Architecture
Heroku Pipelines group multiple applications across distinct deployment stages, typically organizing projects into Review Apps, Staging, and Production. This configuration isolates testing environments from active production systems.
- Review Apps: Automatically deploys an isolated, ephemeral dyno cluster and database for every open pull request on GitHub, allowing QA engineers to test features directly.
- Staging Dynos: An environment that mirrors production data structures and configuration, used for regression testing and load checks before public release.
- Production Dynos: Receives promotion artifacts from staging without recompiling source assets, preventing build inconsistencies between testing and release.
Automating Pipelines via GitHub Actions
While Heroku provides native GitHub integration, many organizations prefer running deployments via independent CI/CD engines like GitHub Actions. This allows engineering teams to execute linting, static analysis, unit tests, and security audits before triggering Heroku builds.
#.github/workflows/deploy.yml
name: Test and Deploy to Heroku

on:
 push:
 branches:
 - main

jobs:
 ci-checks:
 runs-on: ubuntu-latest
 steps:
 - uses: actions/checkout@v4

 - name: Setup PHP Environment
 uses: shivammathur/setup-php@v2
 with:
 php-version: '8.3'
 extensions: mbstring, pdo_pgsql, redis

 - name: Install Dependencies
 run: composer install --prefer-dist --no-progress

 - name: Execute Automated Test Suite
 run: php artisan test

 cd-deploy:
 needs: ci-checks
 runs-on: ubuntu-latest
 steps:
 - uses: actions/checkout@v4

 - name: Deploy to Heroku Remote Engine
 uses: akhileshns/heroku-deploy@v3.13.15
 with:
 heroku_api_key: ${{ secrets.HEROKU_API_KEY }}
 heroku_app_name: 'production-laravel-api'
 heroku_email: 'infrastructure@example.com'
 branch: 'main'
This declarative pipeline prevents broken code from reaching production servers. Decoupling testing pipelines from platform hosting ensures that builds deploy only when all quality criteria are met.
Explore our complete Laravel, Basics directory for more guides.
Factors That Affect Development Cost
- Dyno computing tier (Eco, Basic, Standard, Performance)
- Database scale and high-availability configuration
- Redis cache memory allocation
- Log indexing and external observability data volume
- Egress network bandwidth requirements
A production-grade Laravel setup with high availability and dedicated worker dynos typically spans from $80.00 to over $450.00 monthly on Heroku.
Deploying Laravel to Heroku successfully bridges modern framework capabilities with platform-as-a-service infrastructure. By configuring twelve-factor architecture patterns, decoupling file persistence to cloud object storage, running database migrations through protected release phases, and isolating queue workers from web ingress, engineering teams establish an automated, reliable deployment workflow.
As throughput needs grow, continuous monitoring of PHP-FPM concurrency limits, database connection pool thresholds, and dyno memory consumption provides operational clarity. Balancing PaaS automation against infrastructure expenses helps teams run resilient web applications without the operational overhead of managing physical server instances.