
GitHub Pages is a static site hosting platform integrated directly into GitHub repositories, designed to compile and serve HTML, CSS, client-side JavaScript, and media assets straight from source branches or automated deployment pipelines without requiring dedicated web servers.
Most engineering teams fundamentally misuse GitHub Pages by treating it as an afterthought for toy documentation or basic portfolios. Modern static site generators, decoupled architectures, and automated build pipelines turn GitHub Pages into a distributed, production-grade static edge deployment target. Running standard documentation, component libraries, or public status portals inside dedicated server runtime environments wastes resources and introduces unnecessary maintenance overhead.
This architectural breakdown analyzes the operational boundaries, network delivery mechanics, continuous integration pipelines, and practical static generation workflows required to run performant assets on GitHub Pages without sacrificing backend rigor.
Under the Hood: Network Delivery and Edge Caching Topology
GitHub Pages operates on top of Fastly’s edge CDN infrastructure, backed directly by GitHub’s origin object stores. Understanding this network topology is required when diagnosing latency issues, cache invalidation delays, or deployment state desynchronization.
When a commit triggers a deployment, artifacts are transferred to GitHub’s internal origin storage. Fastly edge nodes front these endpoints, serving static assets through globally distributed Points of Presence (PoPs). Fastly handles TLS termination, HTTP/2 multiplexing, Brotli/Gzip compression, and anycast routing. A request hitting the custom or default domain resolves to a set of anycast IP addresses that route traffic to the nearest topological cache node.
Origin fetches occur only on cache misses. Cache purge signals are triggered when a Pages deployment successfully completes, but stale edge caches can persist depending on proxy behaviors, upstream intermediate resolvers, and custom DNS propagation latencies. Inspecting the edge cache mechanics requires reviewing standard response headers returned during request-response cycles.
curl -I https://username.github.io/repository/\n -H "Accept-Encoding: gzip, deflate, br"\n\nHTTP/2 200\nserver: GitHub.com\ncontent-type: text/html; charset=utf-8\nlast-modified: Wed, 18 Jan 2026 14:12:00 GMT\nx-proxy-cache: MISS\nx-github-request-id: 8B5C:2804:1A882C:22DFB3:65A988D4\nfastly-restarts: 0\nage: 0\nvary: Accept-Encoding\nx-cache: HIT\nx-cache-hits: 1\nx-served-by: cache-chi-kord8230045-CHI\nx-timer: S1705587120.302194,VS0,VE98\nstrict-transport-security: max-age=31536000; includeSubDomains; preloadThe x-cache: HIT and x-served-by headers show edge node termination, while x-proxy-cache exposes the status between GitHub internal ingress nodes and storage buckets. Because Fastly manages stale cache invalidation upon artifact updates, deployments propagate across global nodes within seconds.
System Constraints and Production Boundaries
Operating production-facing assets on GitHub Pages requires designing around hard infrastructure boundaries enforced at the account, repository, and network layers. Deployments that violate these constraints risk throttled bandwidth or terminated builds.
GitHub Pages enforces the following operational limits:
- Artifact Storage Limit: Published sites cannot exceed 1 GB in total size. Repositories containing vast image libraries or unoptimized binary assets will encounter push failures or disabled builds.
- Bandwidth Caps: GitHub enforces a soft bandwidth limit of 100 GB per month. Teams exceeding this limit receive administrative warning notices before traffic throttling.
- Build Execution Timeout: Standard builds and automated custom workflows are bound by a 10-minute timeout per deployment run.
- Rate Limits: Site updates are capped at 10 builds per hour. Continuous deployment triggers that run on every small commit push can quickly exhaust this operational ceiling.
The following matrix compares these baseline specifications against alternative hosting platforms:
| Metric / Feature | GitHub Pages | Cloudflare Pages | AWS S3 + CloudFront |
|---|---|---|---|
| Site Storage Limit | 1 GB | 25 MB per asset / 20k files | 5 TB per object / unlimited bucket |
| Monthly Bandwidth | 100 GB (Soft limit) | Unlimited free bandwidth | Pay-per-GB egress tier |
| Custom Edge Logic | None (Headers preset) | Cloudflare Workers / Functions | CloudFront Functions / Lambda@Edge |
| Automated Builds | GitHub Actions Native | Cloudflare Build Environment | AWS CodePipeline / External CI |
| Custom Domains | Yes (with auto-TLS) | Yes (with auto-TLS) | ACM + Route 53 setup |
These boundaries mean dynamic server-side rendering is impossible natively. All routing logic, authentication, and state management must live entirely client-side or communicate with external APIs.
Jekyll Native Builds vs Custom GitHub Actions Pipelines
Historically, GitHub Pages automatically processed Markdown through a locked-down Jekyll build environment. This legacy pipeline restricts build customization, limits plugins to a verified whitelist, and prevents contemporary build tools from compiling assets. Modern architectures bypass the default Jekyll engine completely.
Disabling the internal Jekyll builder requires placing an empty file named .nojekyll in the root of the published directory or configuring the repository to deploy directly via custom GitHub Actions. Using custom Actions gives teams full control over the runtime environment, allowing Node.js, Go, Rust, or PHP-based static export workflows to build the deployment bundle before dispatching it to Pages.
For engineering teams using cloud workspaces like GitHub Codespaces development environments, building and testing these actions locally simplifies pipeline validation. Standardizing on custom Actions also ensures environment parity between your local containerized toolchain and the remote CI runner.
Choosing custom actions over legacy builds unlocks modern package managers, asset minification tools (such as esbuild and Vite), static site generators (like Astro, Hugo, or Next.js static exports), and automated validation steps prior to site publication.
Building a Production-Grade GitHub Actions Deployment Workflow
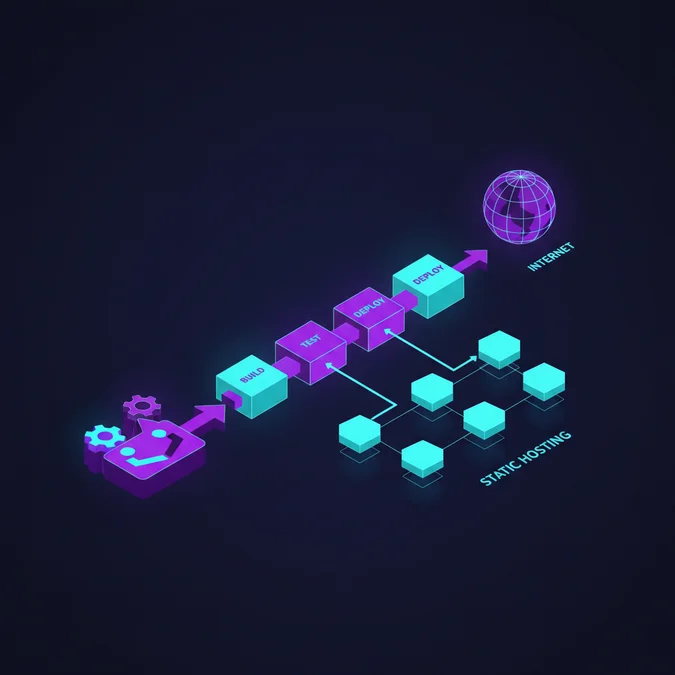
Deploying static artifacts via GitHub Actions requires using GitHub’s native Pages actions: actions/configure-pages, actions/upload-pages-artifact, and actions/deploy-pages. This eliminates the legacy pattern of committing build artifacts back into a gh-pages Git branch.
The workflow below shows a multi-step compilation process that checks out code, sets up an environment, runs asset compilation, verifies output integrity, and deploys the generated bundle:
name: Deploy Static Distribution to Pages\n\non:\n push:\n branches:\n - main\n workflow_dispatch:\n\npermissions:\n contents: read\n pages: write\n id-token: write\n\nconcurrency:\n group: 'pages'\n cancel-in-progress: true\n\njobs:\n build:\n runs-on: ubuntu-latest\n steps:\n - name: Checkout Source Repository\n uses: actions/checkout@v4\n\n - name: Setup Node.js Runtime\n uses: actions/setup-node@v4\n with:\n node-version: 20\n cache: 'npm'\n\n - name: Install Dependencies\n run: npm ci\n\n - name: Compile Static Distribution\n run: npm run build\n\n - name: Ensure.nojekyll File Exists\n run: touch./dist/.nojekyll\n\n - name: Upload Pages Artifact\n uses: actions/upload-pages-artifact@v3\n with:\n path: './dist'\n\n deploy:\n environment:\n name: github-pages\n url: ${{ steps.deployment.outputs.page_url }}\n runs-on: ubuntu-latest\n needs: build\n steps:\n - name: Deploy Artifact to GitHub Pages\n id: deployment\n uses: actions/deploy-pages@v4The concurrency configuration block is critical. Setting cancel-in-progress: true prevents race conditions when multiple pushes occur in quick succession. This ensures that only the latest build completes deployment, preventing stale artifacts from overwriting current code.
Custom Domains, DNS Topologies, and TLS Termination Mechanics
Pointing a custom domain to GitHub Pages requires configuring specific DNS records and verifying domain ownership to avoid subdomain hijacking attacks. GitHub issues automated Let’s Encrypt certificates, managing renewal rotations without manual intervention.
For apex domains (such as example.com), configure standard A records pointing to GitHub Pages IP infrastructure. GitHub provides four anycast IPv4 addresses and four IPv6 addresses to ensure high availability:
185.199.108.153185.199.109.153185.199.110.153185.199.111.1532606:50c0:8000:1532606:50c0:8001:1532606:50c0:8002:1532606:50c0:8003:153
For subdomains (such as docs.example.com), configure a canonical name (CNAME) record targeting your GitHub user or organization domain:
; CNAME Record for Subdomain Configuration\ndocs.example.com. 300 IN CNAME your-org.github.io.To establish ownership and prevent domain hijacking, configure a TXT record in your DNS zone pointing to your GitHub verification token:
; TXT Record for Domain Verification\n_github-pages-challenge-your-org.example.com. 300 IN TXT "1a2b3c4d5e6f7a8b9c0d"Once DNS propagation finishes, enable Enforce HTTPS in the repository settings. GitHub will validate the challenge token, issue the TLS certificate via ACME, and configure HTTP to HTTPS 301 redirects across edge nodes.
Single Page Application (SPA) Routing Workarounds
A primary limitation of GitHub Pages is its static file resolution model. When a visitor navigates directly to a client-side route like /dashboard/analytics, the edge server searches for a physical file located at /dashboard/analytics/index.html. If no such file exists, GitHub Pages immediately returns a standard 404 response.
Because GitHub Pages does not allow custom URL rewriting rules via server configuration files (like .htaccess or Nginx config blocks), engineers must implement client-side routing fallback patterns. The most durable solution involves using the fallback mechanics of a custom 404.html file.
When a 404 occurs, GitHub Pages serves the root 404.html file with a 404 HTTP status code. By embedding a script inside this file, the path segments can be captured and encoded into query parameters, redirecting the browser back to the root entry point index.html where the client router restores the intended state.
<-- 404.html SPA Redirection Script -->\n<DOCTYPE html>\n<html>\n <head>\n <meta charset="utf-8">\n <title>Redirecting..</title>\n <script>\n // Extract URL path segments and convert them to query parameters\n var pathSegmentsToKeep = 0;\n var l = window.location;\n l.replace(\n l.protocol + '//' + l.hostname + (l.port? ':' + l.port: '') +\n l.pathname.split('/').slice(0, 1 + pathSegmentsToKeep).join('/') + '/?p=' +\n l.pathname.slice(1).split('/').slice(pathSegmentsToKeep).join('/').replace(/&/g, '~and~') +\n (l.search? '&q=' + l.search.slice(1).replace(/&/g, '~and~'): '') +\n l.hash\n );\n </script>\n </head>\n <body></body>\n</html>Inside your application root (index.html), place the complementary restoration logic before your client router mounts:
// index.html Path Restoration Script\n(function(l) {\n if (l.search[1] === 'p') {\n var decoded = l.search.slice(1).split('&').map(function(s) {\n return s.replace(/~and~/g, '&')\n }).filter(function(v) {\n return v.slice(0, 2) === 'p='\n })[0];\n \n if (decoded) {\n window.history.replaceState(null, null,\n l.pathname.slice(0, -1) + decoded.slice(2) +\n (l.search? '?' + l.search.slice(1): '') +\n l.hash\n );\n }\n }\n}(window.location));While functional, this approach returns a 404 HTTP status header to search crawlers before client-side hydration redirects the user. For SEO-critical applications, pure static export (generating physical HTML files for every route) is preferred over SPA routing fallbacks.
Exporting Dynamic Backend Frameworks to GitHub Pages
While dynamic application logic belongs on dedicated application servers, documentation, static client portals, and administrative dashboards derived from backend frameworks can be compiled to static assets and served via GitHub Pages.
For instance, when engineering teams design internal operations consoles or point-of-sale architectures, as outlined in our guide on building custom POS systems with Laravel, customer-facing API catalogs or static audit log viewers can be decoupled and hosted on GitHub Pages. This offloads static asset delivery entirely from the central transactional database and web tier.
To bridge backend documentation tools into GitHub Pages, static generation workflows can crawl and serialize dynamic endpoints during CI execution. The following build script demonstrates fetching OpenAPI schemas, compiling API documentation into static HTML bundles, and staging them for publication:
#!/usr/bin/env bash\nset -euo pipefail\n\necho "Initializing static export pipeline.."\nmkdir -p./dist/api-docs\n\n# Fetch current OpenAPI specifications from the backend runtime\ncurl -s https://api.internal.domain/v1/openapi.json -o./dist/api-docs/openapi.json\n\n# Compile static redoc documentation distribution\nnpx @redocly/cli build-docs./dist/api-docs/openapi.json -o./dist/api-docs/index.html\n\n# Inject robots.txt to restrict crawling on preview subdomains\ncat <<EOF >/dist/robots.txt\nUser-agent: *\nAllow: /\nSitemap: https://docs.example.com/sitemap.xml\nEOF\n\necho "Static bundle generated successfully at./dist"Decoupling operational documentation from backend production runtimes eliminates zero-day vulnerability attack surfaces in documentation tooling and guarantees that documentation remains available even during backend maintenance windows.
Security Posture, Access Control, and Header Customization Limitations
Securing assets on GitHub Pages requires acknowledging its permission boundaries. Public repositories on GitHub offer public GitHub Pages sites. GitHub Enterprise Cloud and GitHub Enterprise Server allow repositories to restrict Pages visibility to authenticated organization members, but standard accounts lack this feature.
The lack of native HTTP response header customization is a major security consideration on GitHub Pages. You cannot define custom headers natively, meaning you cannot enforce custom values for:
Content-Security-Policy(CSP)X-Frame-OptionsX-Content-Type-OptionsPermissions-PolicyCross-Origin-Opener-Policy(COOP)
Engineers must instead enforce these security boundaries using HTML <meta> tags inside the compiled documents:
<head>\n <meta charset="utf-8">\n <meta http-equiv="Content-Security-Policy" content="default-src 'self'; script-src 'self' https://trustedscripts.com; style-src 'self' 'unsafe-inline'; img-src 'self' data: connect-src 'self' https://api.example.com;">\n <meta http-equiv="X-Content-Type-Options" content="nosniff">\n <meta name="referrer" content="strict-origin-when-cross-origin">\n</head>Keep in mind that certain security directives, such as the frame-ancestors directive, cannot be enforced via HTML meta tags and require server-level header responses. If strict header security is an audited requirement, GitHub Pages must sit behind an edge proxy like Cloudflare, which injects the missing response headers before returning traffic to the client.
Troubleshooting Common Build Failures and Deployment Anomalies
When troubleshooting deployment pipelines on GitHub Pages, specific failure patterns occur repeatedly. Diagnosing these issues requires understanding the boundary between the Actions runner and the Pages deployment controller.
Deployment Pipeline Permissions Failures
If your workflow fails during the deployment phase with an HTTP 403 error, the deployment token lacks necessary write access. You must explicitly configure the permissions block inside your workflow YAML file:
# Required permissions for GitHub Pages deployment\npermissions:\n contents: read\n pages: write\n id-token: writeWithout id-token: write, OpenID Connect (OIDC) token exchange fails, preventing the deployment job from authenticating against the internal Pages deployment service.
Case-Sensitivity Path Resolution Bugs
Local development environments running on macOS or Windows operate on case-insensitive filesystems by default. An asset requested as ./images/logo.PNG will load locally even if the file on disk is named logo.png. However, the GitHub Pages origin environment runs on Linux, where paths are case-sensitive. This mismatch leads to broken assets and 404 errors in production.
To catch these issues in CI, run a link and file audit step during your build workflow:
# Lint files for casing discrepancies and broken relative references\nnpx broken-link-checker http://localhost:8080/ -ro --filter-level 3Underscore Path Ingestion Failure
By default, if an artifact contains folders starting with an underscore (such as _app or _next), GitHub Pages assumes Jekyll rules apply and ignores them during deployment. Ensure a .nojekyll file exists in the deployment bundle root to prevent this automated filtering.
Architectural Exploration and Directory Hub
Navigating modern software delivery patterns requires mastering both client-side static architectures and backend execution environments. Choosing when to deploy decoupled static sites versus dynamic full-stack clusters determines long-term maintenance costs, delivery performance, and infrastructure stability.
For further architectural breakdowns, deployment deep-dives, and runtime tutorials, visit our master directory: [Explore our complete Laravel, Basics directory for more guides.](/topics/topics-laravel-basics/)
GitHub Pages remains one of the most reliable and cost-effective hosting platforms for documentation, single-page frontends, and static artifacts when paired with modern GitHub Actions workflows. Understanding its Fastly-backed edge delivery model, adhering to storage and rate limits, and securing assets through explicit headers ensures predictable production operations.
Before choosing GitHub Pages for an architectural project, verify that your application does not require dynamic server logic, non-standard HTTP header injection, or strict private repository access on free-tier accounts. For decoupled frontends and high-performance asset delivery, standardizing on automated CI pipelines and direct artifact deployment delivers robust reliability with minimal operational overhead.